Production-ready AMIs, deployable in minutes.
Amazon Machine Images hardened, tuned and documented for the stacks you already trust — with a cloud toolset to keep them spotless.
Built on the stacks you already know
- Ubuntu
- nginx
- MariaDB
- PHP 8.3
- Zabbix
- Nagios
- systemd
Our AMIs
Prebuilt, pre-tuned base images. Pick a stack, launch it and forget the boring parts.
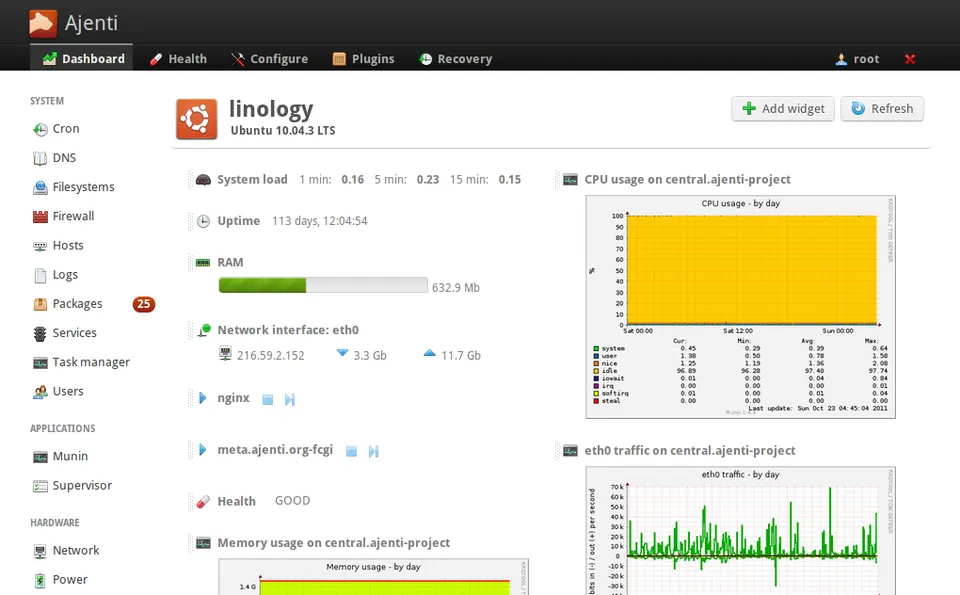
Ajenti 1.2
A server control panel built on Ajenti V1 and the Ajenti-V module: simple, secure and fast shared-hosting management, already installed and configured.
Memcached Hardened
Hardened, production-ready Memcached: mandatory SASL, firewall on by default and unattended security updates.
Ubuntu 22.04 LTS Hardened
Life insurance for your entire Ubuntu 22 fleet: a hardened AMI, maintained when nobody else maintains it.
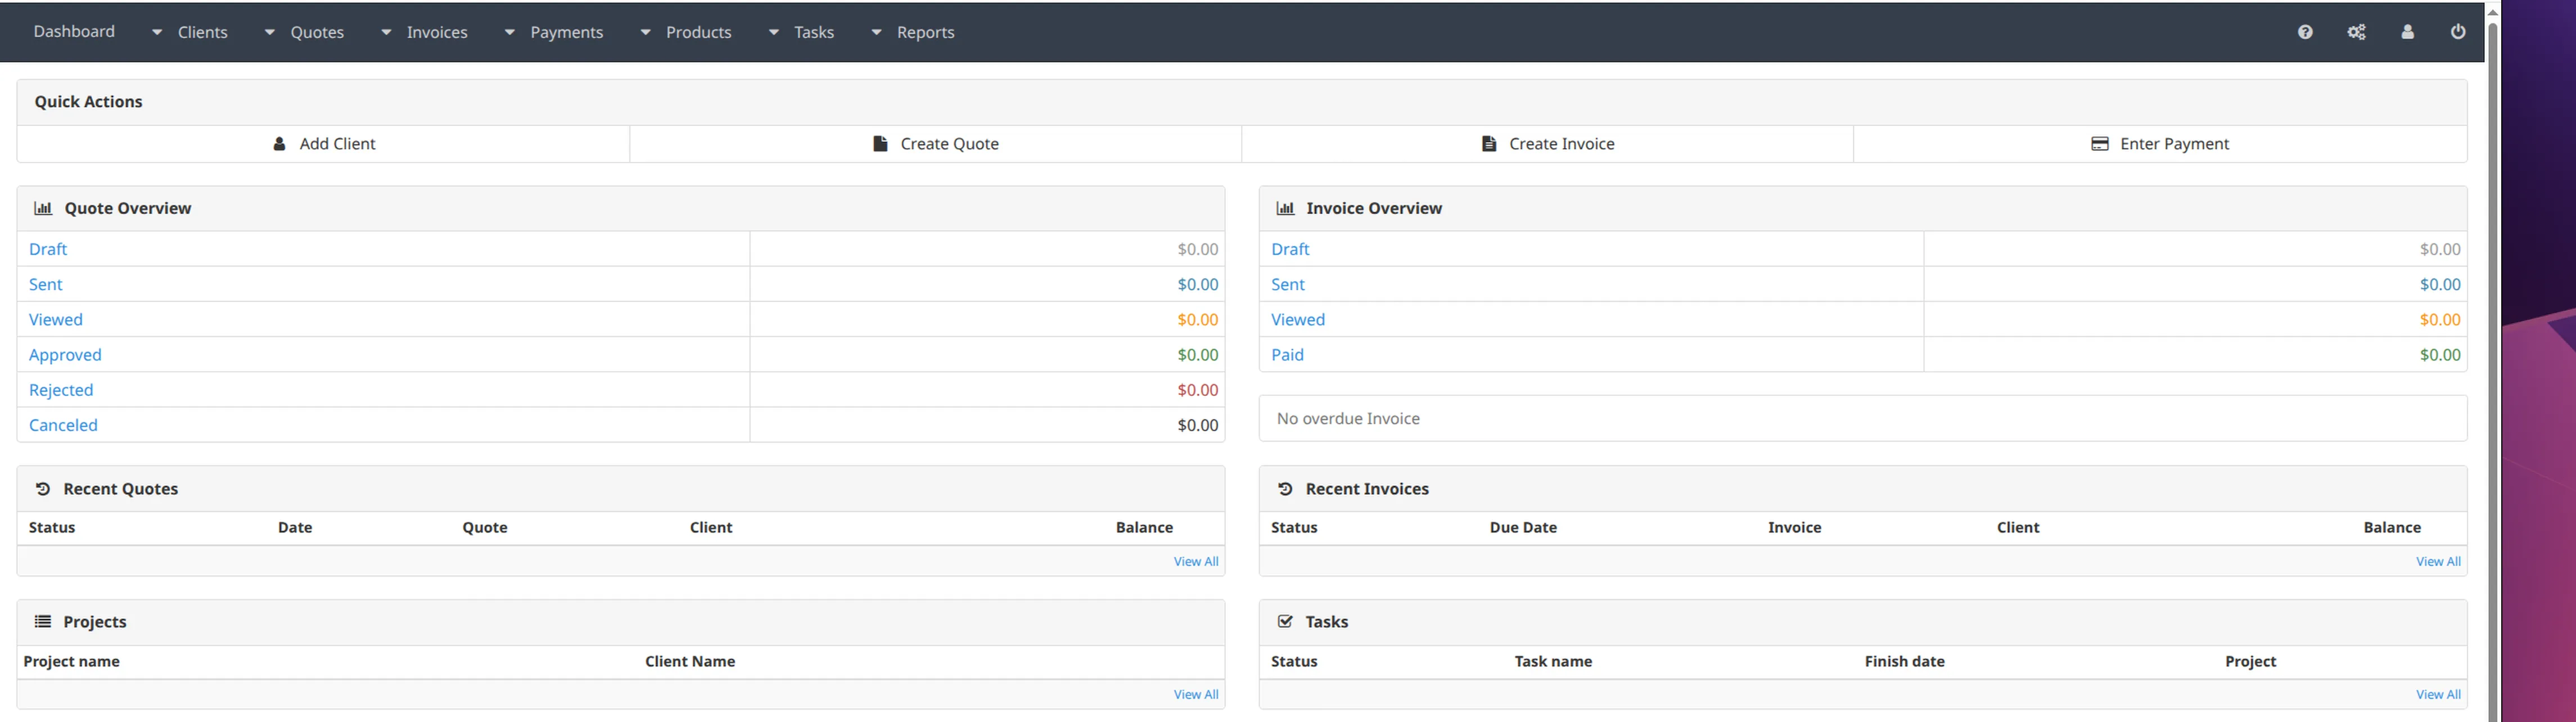
InvoicePlane 1.6
Manage quotes, invoices, clients and payments with InvoicePlane, installed and configured on Ubuntu 24.04 with nginx, PHP 8.1 and MariaDB 11.4.
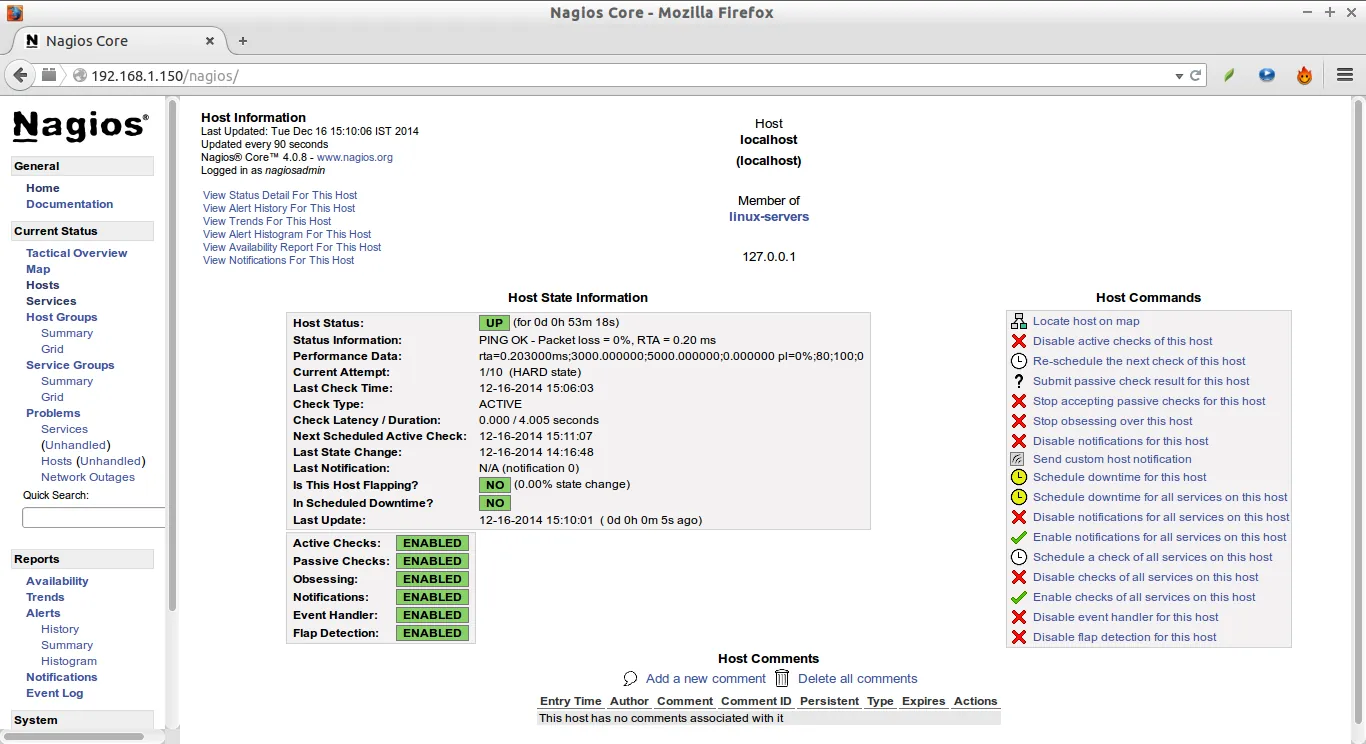
Nagios 4
Nagios 4 and NagiosGraph installed and configured, served by nginx: end-to-end infrastructure monitoring from the very first boot.
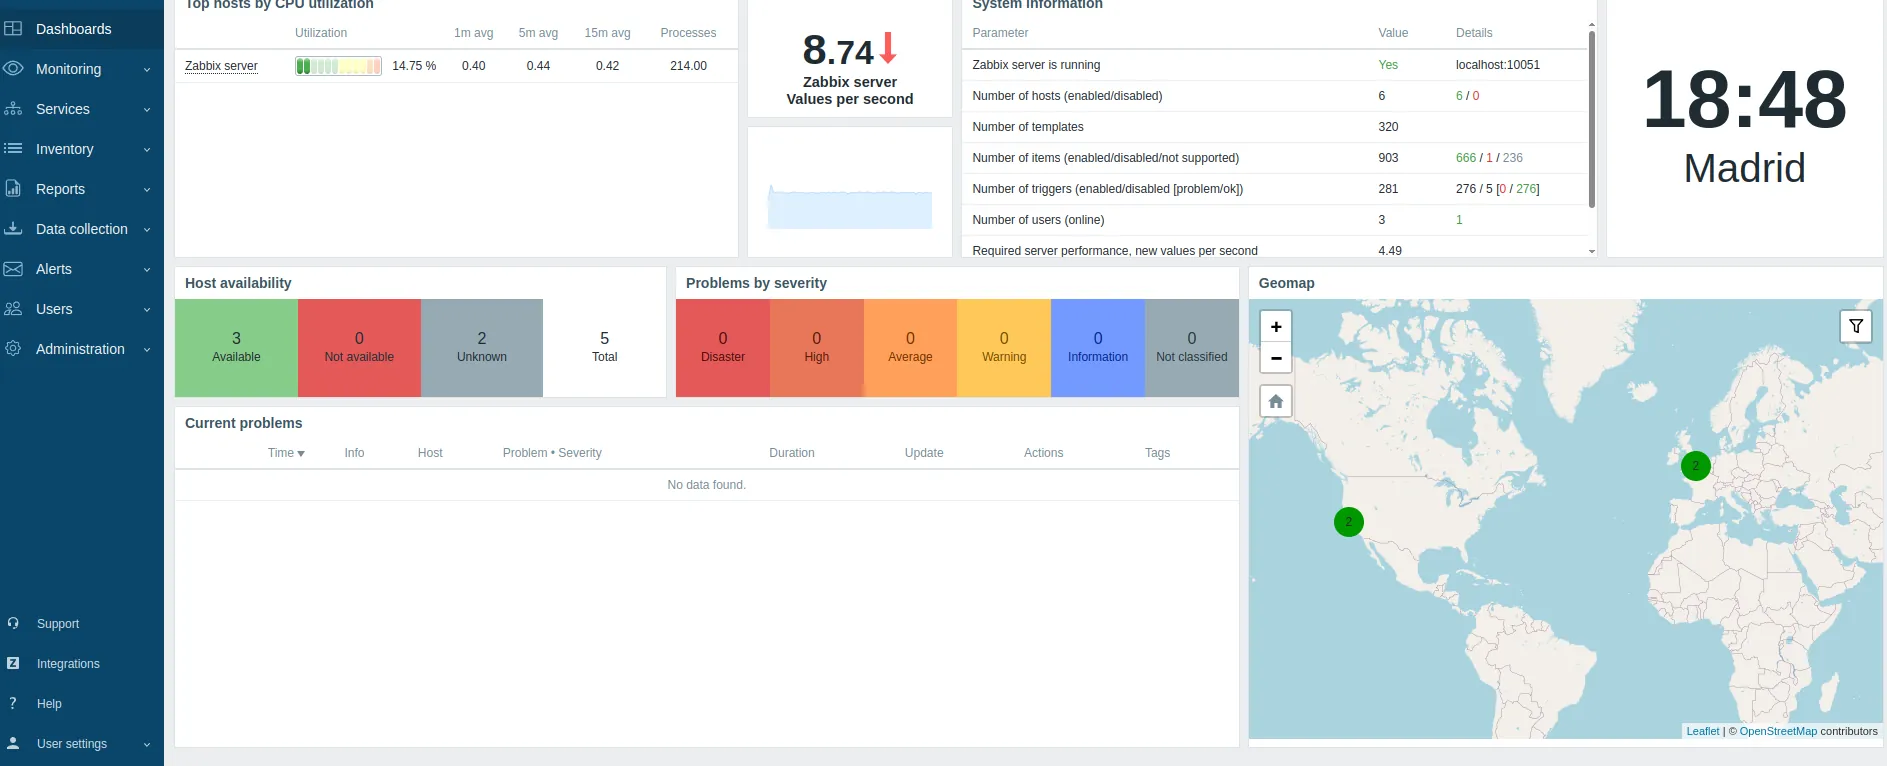
Zabbix Server
A production-ready Zabbix server and web frontend, with AWS SNS notifications, Auto Scaling group support and CloudFormation stacks that create the resources for you.
Bitnami is gone. We keep maintaining.
Drop-in AMI replacements for the Bitnami stacks teams relied on most — patched every week, audited daily, and with a real person on the other end.
Imaxe tool.
Forget maintaining ten scripts scattered across every AMI. imaxe is the operations console for your instances: a single binary that discovers, installs and orchestrates specialized modules — TLS, mail, backups, monitoring — all idempotent, all auditable.
15 modules, a single binary
One binary discovers, installs and orchestrates every module. Add one and it shows up here on its own.
TLS
Issue and renew free <strong>Let's Encrypt</strong> certificates for your server and reload them without interrupting service. One command gets it going; from then on it renews itself.
System
Keeps the operating system <strong>up to date and properly set up</strong>: updates (and unattended upgrades), language, time zone, machine name and synchronized time. All with a handful of clear commands.
SSH
Manage your server's remote access without editing files by hand: <strong>authorized keys</strong>, <strong>host keys</strong>, active sessions and <strong>sshd hardening</strong>, all with a configuration check before reloading.
Configure the server's <strong>outbound mail</strong> through a smarthost (SES, a corporate relay…) and confirm it works with a test send. One command sets it up; from then on, your system notifications actually go out.
Alerts
Publishes the instance's important notices —intrusions, a full disk, a service down— to a <strong>shared SNS topic</strong>. The operator and the other modules use it as their <strong>single channel</strong>: severity threshold, deduplication and a retry queue if SNS does not answer.
Secrets
Generates, reads and rotates the <strong>instance's secrets</strong> (passwords, passphrases, keys) with a CSPRNG and <code>0600</code> permissions. Idempotent across mass-produced AMIs: <code>generate</code> creates the secret only if it doesn't exist, and <code>get</code> gives clean output for a <em>pipe</em>.
Firewall
Check the status of <strong>ufw</strong>, block abusive IPs by hand, and open or close ports with a single command. Automatic bans are handled by <strong>fail2ban</strong>; this is for your manual blocks and port rules.
Fail2ban
Check and manage <strong>fail2ban</strong> bans from a single command: see which jails are active, who is banned, ban or unban IPs by hand and unblock in a pinch. Without remembering the syntax of <code>fail2ban-client</code>.
Inventory
Probes the machine and writes a <strong>readable inventory</strong> with the operating system, the installed software and its versions, the database and the imaxe product in <code>/etc/imaxe/info.yaml</code>. No secrets, no surprises: one command and you know exactly what you have.
Lynis
Runs a <strong>CIS hardening</strong> audit on your server and returns an actionable report: a hardening index, the <strong>warnings</strong> to resolve and concrete suggestions, each with its <em>test id</em> so you know exactly what to touch.
Integrity
Monitor <strong>file integrity</strong> with AIDE: it stores a reference snapshot (baseline) of the system and alerts you to any added, deleted or modified file. One command checks the state; you decide when to accept the changes as normal.
rkhunter
Scans the system with <strong>rkhunter</strong> for rootkits, backdoors and altered files, and gives you a clear summary of the <strong>warnings</strong>. Manages the properties baseline and keeps the signatures up to date with a single command.
ClamAV
Scan files and directories for <strong>malware</strong> with the <strong>ClamAV</strong> engine, isolate what's infected in quarantine and keep the signatures current with <strong>freshclam</strong>. One command scans; another updates — no surprises.
Audit
Query <strong>auditd</strong> events and manage the <strong>CIS</strong> audit rules with readable commands — without memorizing the syntax of <code>auditctl</code> or <code>ausearch</code>. See who logged in, what was touched and which rules are loaded at a glance.
Memcached
Works out and applies the <strong>cache size</strong>, threads and connections that suit your instance, manages the <strong>SASL credentials</strong> and the <strong>TLS certificate</strong>, and shows the service status live — all without hand-editing <code>memcached.conf</code>.
No surprises: you pay on your AWS bill
Every AMI states its model on its page and on AWS Marketplace. No contracts, no separate card: everything settles in your AWS account.
Cloud cost only
Several catalog AMIs carry no software cost: you pay only for the cloud instance you choose.
- Frequent patching included
- Complete documentation
- No instance limit
From US$0.05/h
AMIs with a software cost are billed per hour of use, metered by AWS Marketplace. Stop the instance and you stop paying.
- Free trial available
- Daily CVE audit
- Ticket support included
Dedicated support
For fleets and legacy cases: an annual subscription with priority support from the team that builds the images.
- Response SLA
- Migration assistance
- Direct line to engineering
The exact price of each AMI appears on its page and on AWS Marketplace before you launch.
Need something that isn't in the catalog? We build it with you.
We build custom AMIs and complete infrastructures on AWS: your stack, your hardening, your network — with the same weekly maintenance as the rest of the catalog. Tell us what you need and we'll propose a solution.
Hardened, tuned and documented. Under your control.
Every AMI arrives production-ready: no manual installs, no guessing parameters. Just launch it and connect.
Optimized for any workload, in any region
Deploy faster, reduce the attack surface and simplify day-to-day operations.
Hardened to CIS
CIS Level 1 profile verified daily. Zero open CVEs across the active catalog.
Native on AWS
Built-in SQS auto-scaling and SNS alerts. Fits into an EC2 fleet without glue.
Weekly patching
Security updates applied to the base image every week, hands-off.
Human support
Tickets that reach the team that builds the images. No bots, no tier one.
Numbers you notice from the very first boot
From launch to running
Average boot time until the service accepts traffic. Deploy and connect.
CIS benchmark
Hardening verified daily on Ubuntu LTS, without losing functionality.
open CVEs
Automated audit every day and weekly patches across the entire active catalog.
The complete solution for servers that don't give you scares
Hardened base
Ubuntu LTS with a CIS Level 1 profile, minimal packages and a compacted journal.
Managed services
Everything under systemd, with controlled restarts and built-in health checks.
Auto-scaling
EC2 instance registration and deregistration via SQS, no scripts scattered across the fleet.
SNS alerts
Native AWS notifications classified by severity with a single config line.
Backups and rotation
Daily log rotation and snapshot hooks via cron, ready out of the box.
Multilingual
Frontends ready in several languages, switchable per user.
We brought up the new Zabbix, restored the dump and moved the EIP in an afternoon. SQS auto-scaling worked on the first try and support replied in under two hours.
Launch your first AMI today
Hardened images, clear documentation and human support. Choose where to start.
Read the documentation
Concrete guides for installation, configuration and migration.
Go to documentation